
Maximize your Microsoft security with 24/7 monitoring and incident response
Your Microsoft security platform generates vast amounts of security data every day. Microsoft Defender EDR, part of the Microsoft XDR ecosystem, correlates signals from endpoints, identities, email, cloud environments and applications into security incidents. However, effectively interpreting and responding to these incidents remains a challenge for many organizations.
With the Microsoft Security Center module within SecureSIGHT, you gain not only full visibility into your Microsoft security environment, but also the support of the Secutec Security Operations Center (SOC) for continuous monitoring, analysis and incident handling.
We transform your security data into actionable insights that strengthen your cyber resilience, helping you get the maximum value from your Microsoft security investments.

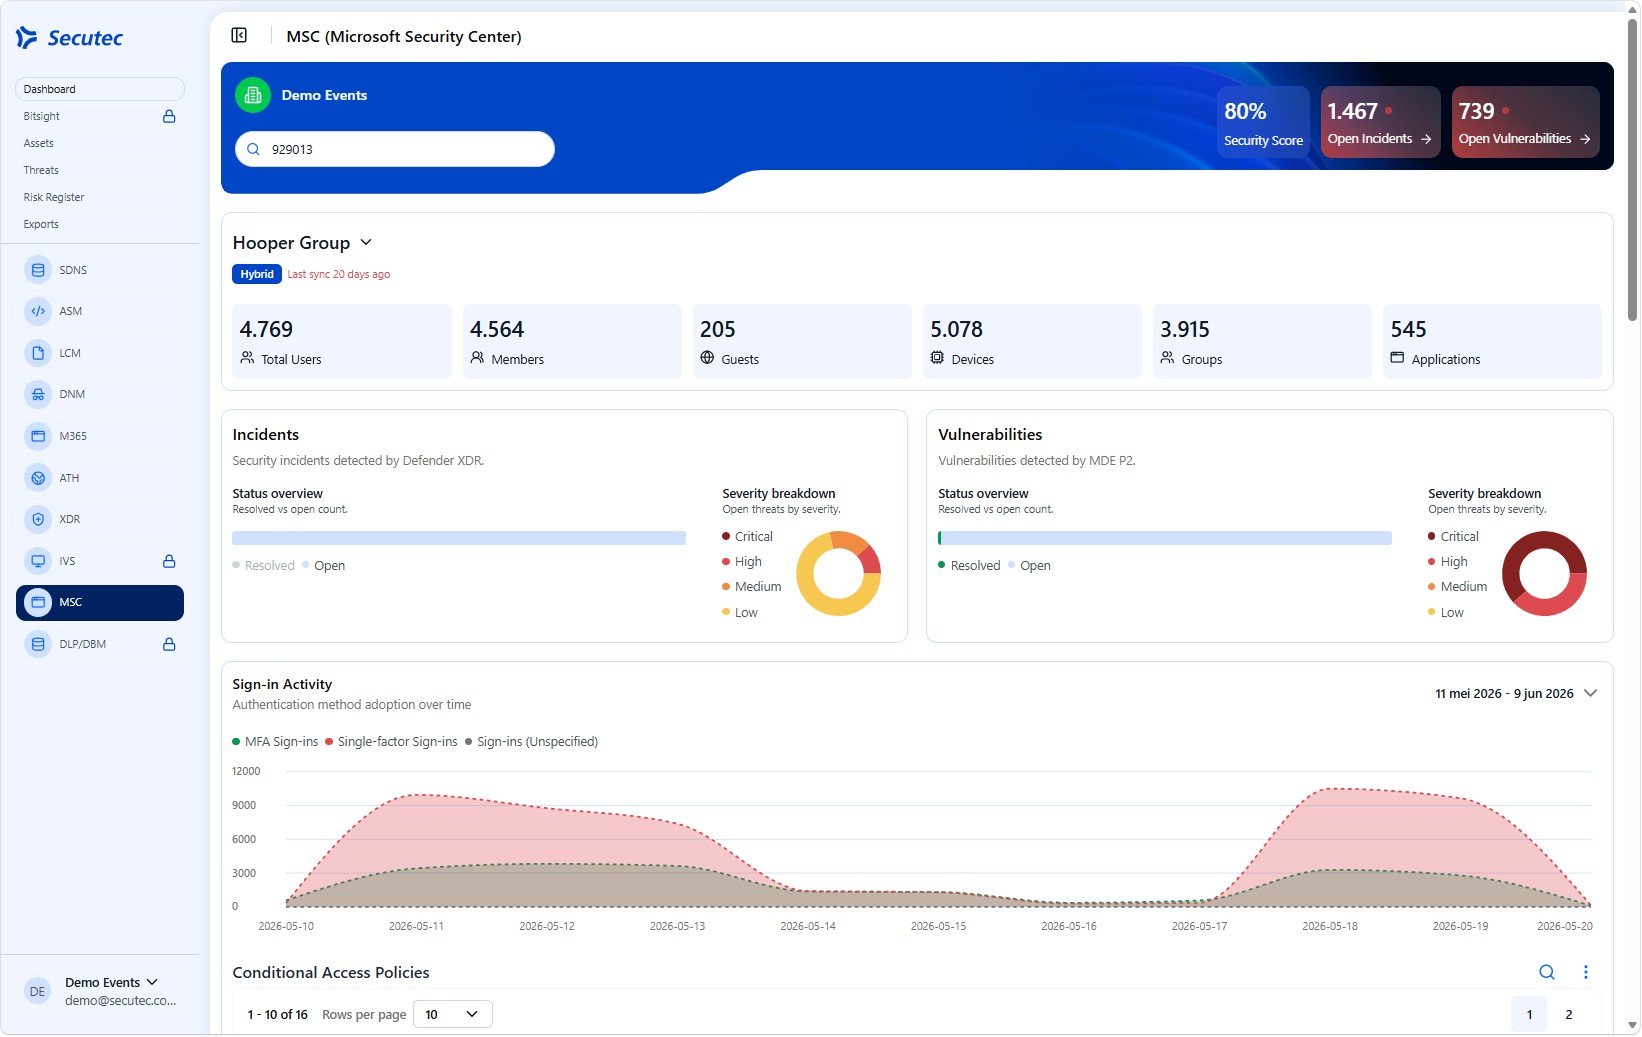
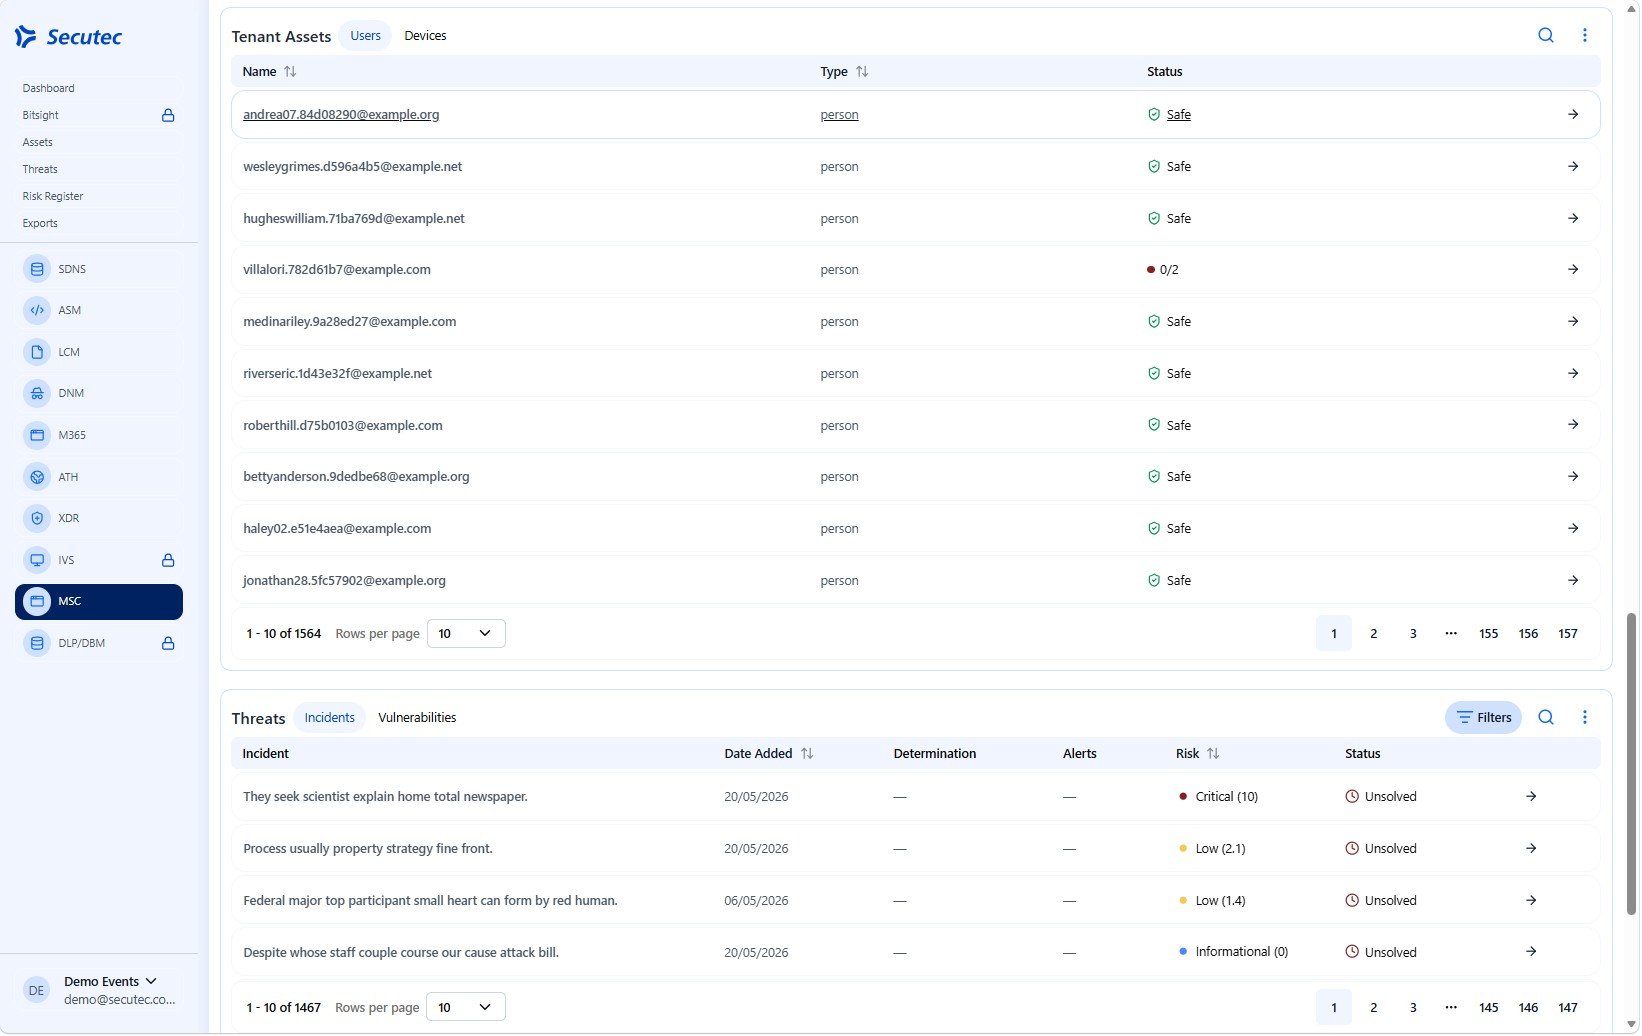
Centralized Visualization of Microsoft Defender EDR Incidents
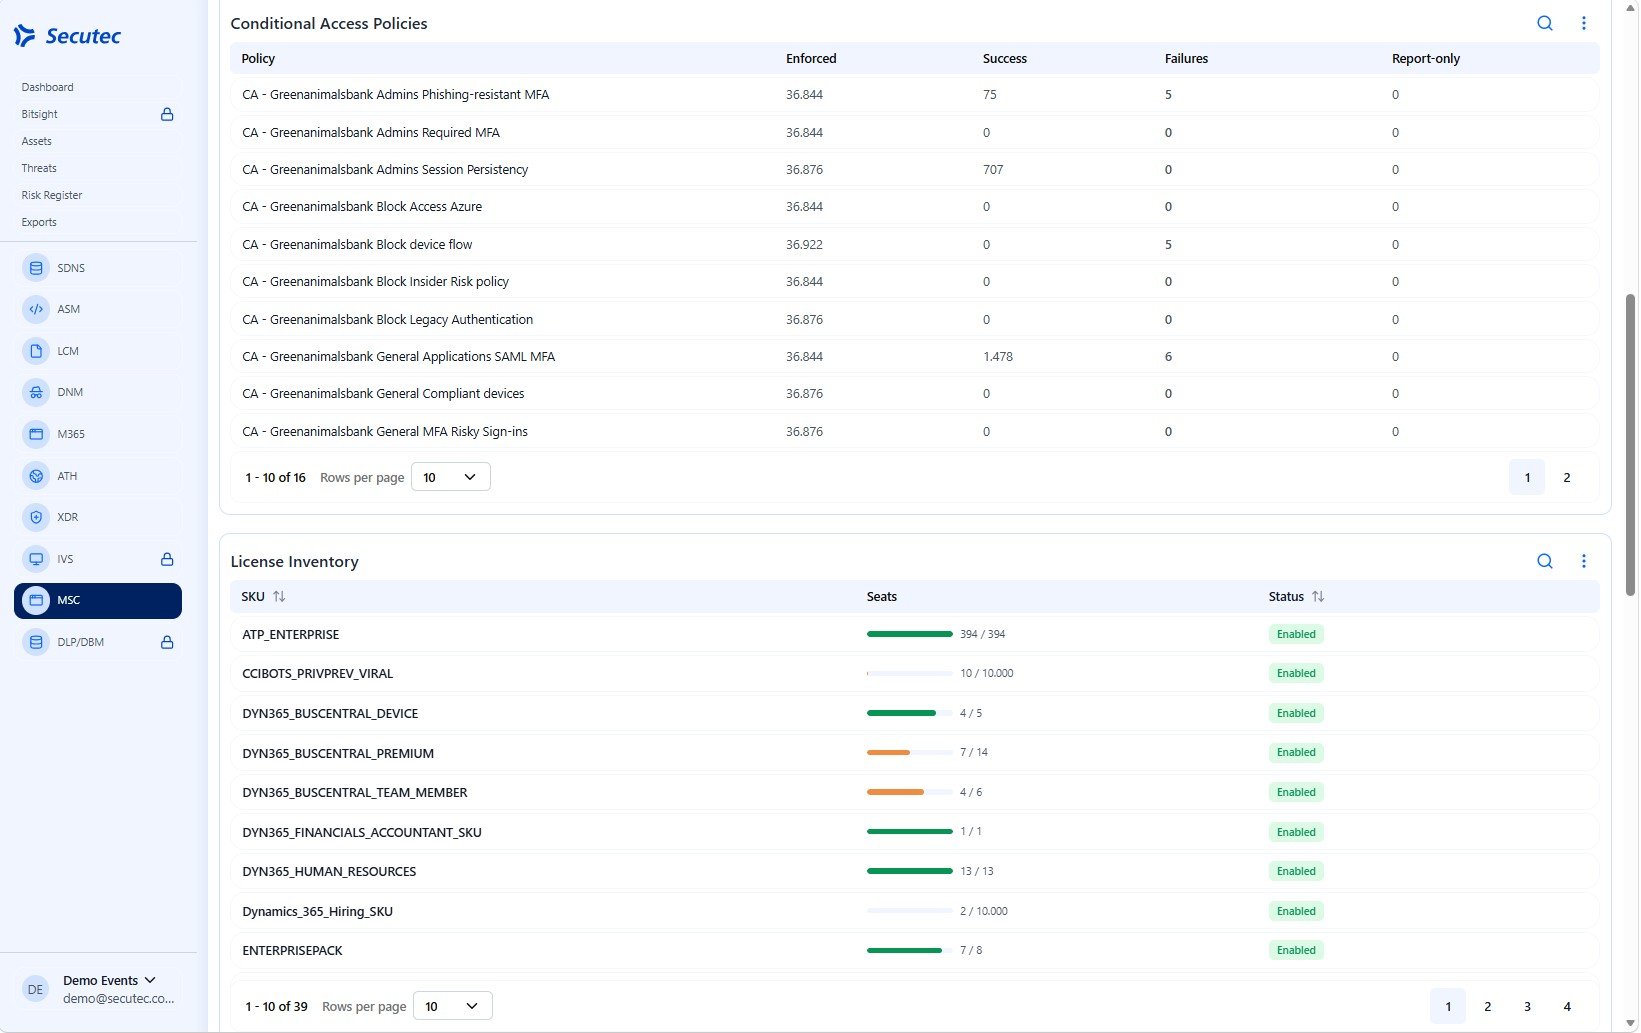
SecureSIGHT collects and visualizes incidents, alerts and threat intelligence from your Microsoft Security Center environment, presenting everything in a single, intuitive platform.
The module consolidates data from:
- Microsoft Defender for Endpoint
- Microsoft Defender for Identity
- Microsoft Defender for Office 365
- Microsoft Defender for Cloud Apps
- Microsoft Security Exposure Management
- Microsoft Defender Vulnerability Management
This provides a comprehensive overview of active threats, suspicious activities and security incidents across your organization.
Why Choose SecureSIGHT’s Microsoft Security Center & 24/7 Managed SOC?
-
24/7 Managed SOC Service
Your Microsoft security environment is continuously monitored by our experienced security analysts. This gives your organization access to a skilled cyber defense team without the need to build and maintain your own SOC.
-
From isolated alerts to full attack context
Security teams often lose valuable time analyzing individual alerts.
Microsoft Defender EDR automatically correlates alerts into incidents and full attack stories. SecureSIGHT enhances this by enriching, visualizing and contextualizing that information.You gain insight into:
- The full attack chain
- Involved users, endpoints and systems
- Incident impact and severity
- Priority risks and threats
- Incident evolution over time
This leads to faster decision-making and more efficient incident response.
-
Faster Detection, faster response
When a serious security incident occurs, every minute counts.
The Secutec SOC provides support for:- Account compromises
- Malware and ransomware incidents
- Suspicious login activity
- Privilege escalation attacks
- Phishing-related incidents
- Endpoint and identity-based threats
Through continuous monitoring and specialized analysis, threats are identified earlier, enabling faster and more effective response actions.
-
Less Alert Fatigue, More Focus
Many organizations face hundreds or even thousands of security alerts each month. Distinguishing real threats from noise requires expertise and continuous attention.
SecureSIGHT helps to:
- Identify relevant incidents faster
- Prioritize threats more effectively
- Reduce false positives
- Relieve pressure on security teams
- Respond more efficiently to critical events
This allows internal teams to focus on their core responsibilities while ensurig that critical security incidents receive the attention they need.
-
Management Reporting
In addition to operational monitoring, SecureSIGHT provides valuable management-level insights.
Clear dashboards and reports offer visibility into:
- Incident trends
- Threat levels
- Risk evolution
- Opportunities for security improvement
This ensures that both IT teams and management have the information they need to make informed decisions.
"We transform your security data into actionable insights that strengthen your cyber resilience, helping you maximize the value of your Microsoft security investments."
24/7 Managed SOC Service
Your Microsoft security environment monitored by experienced analysts
Technology alone is not enough to detect and stop cyber threats in time.
That's why the Microsoft Security Center module is backed by the Secutec SOC, which monitors your Microsoft security environment 24/7.

Fully Integrated within SecureSIGHT
The Microsoft Security Center module integrates seamlessly with other SecureSIGHT modules, including:
- M365 (continuous tenant security configuration checks)
- Active Threat Hunting
- Attack Surface Management (ASM)
- Leaked Credentials & Dark Web Monitoring
- SecureDNS
This creates a single, centralized platform for managing cyber risks, security incidents and operational security processes.
Take control of your Microsoft security
Discover how our innovative technologies help safeguard your digital assets.